Go Beyond SIEM With AI-Powered Security Operations
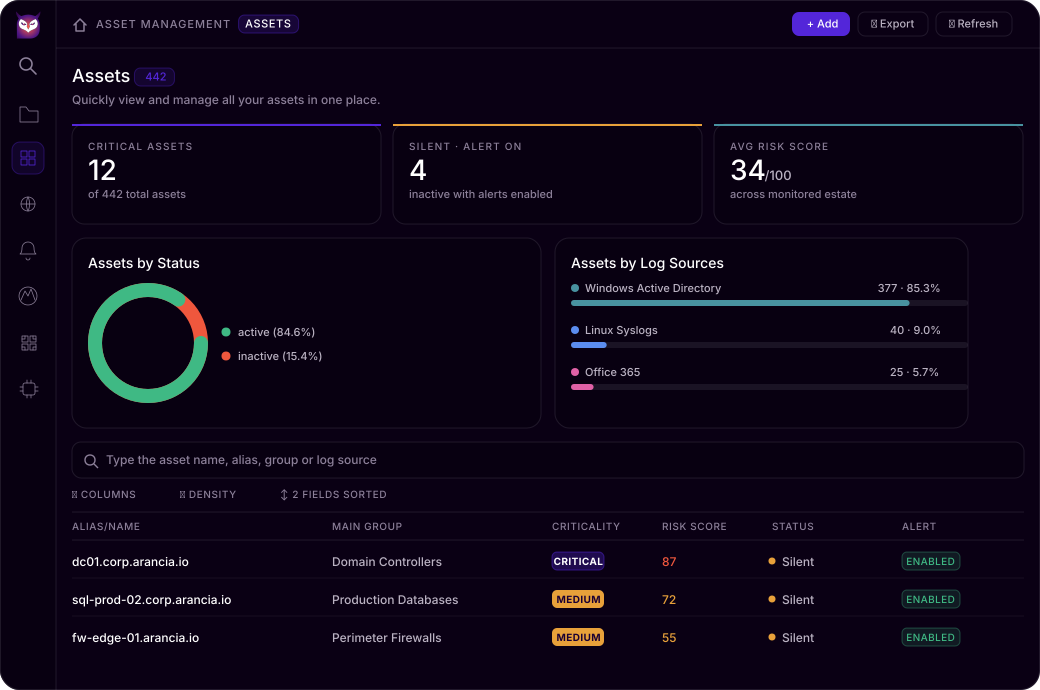
DarkSense is Arancia's AI-powered cybersecurity operations platform
DarkSense brings together SIEM, SOAR, threat intelligence, detection, threat hunting, exposure management, investigation, and automated response into a unified platform backed by 24/7 security operations.
The business benefit is a shift from simply collecting and detecting security events to continuously investigating, containing, and reducing cyber risk.
- Next-Generation SIEM & Log Management
- AI-Assisted Detection, Investigation & Correlation
- Security Automation & SOAR
- Automated Threat Containment and Response
- 24/7 SOC / MDR Integration
- Proactive Threat Hunting
- Threat Intelligence
- Multi-Tenant Security Operations
- Incident Investigation & Case Management
- Exposure / Attack Surface Management
- Vulnerability & Risk Management
- Dark Web / Credential / Brand Monitoring
- Compliance Visibility & Reporting
- Cloud, Identity, Endpoint and Network Visibility
One intelligent platform, from signal to response
DarkSense provides full visibility into the data that is being ingested along with Autonomous AI decisions and containments.
Your technology footprint
All telemetry ingested & aggregated
Cloud Assets
SASE / CASB / ZTNA
EDR
Firewall
Vulnerability Mgmt
SIEM (existing)
Applications
IoT & OT Assets
Email Gateways
IAM / PAM
DarkSense Platform
Full autonomous cybersecurity platform
- Ingestion
- Data Pipeline
- Detection & Correlation
- Threat Intelligence
- Autonomous AI SOC
- Response
Arancia SOC-as-a-Service
Predict AI Early-Warning Risk Score
Exposure & Vulnerability Management
EASM, Dark Web & DRP
Audit & Configuration Data
SOC Dashboard
Threat Hunting & Incident Response
Managed Detection & Response (MDR)
24 / 7 / 365 Coverage
Delivery Models That Scale With You
DarkSense Platform+
DarkSense Platform+ provides the DarkSense cybersecurity operations platform and Next-Generation SIEM for organizations with their own SOC or security team. Customers operate and manage the platform directly, maintaining control over security monitoring, detection, investigation, and response across their environment.
- Next-Generation SIEM & Log Management
- Security Data Lake & Long-Term Retention
- Detection Engineering & Correlation
- Autonomous SOC Investigation & Triage
- SOAR & Automated Response
- Threat Intelligence
- Proactive Threat Hunting
- Case & Incident Management
- Exposure / Attack Surface Management
- Vulnerability & Risk Visibility
- Dark Web & Credential Monitoring
- Compliance Dashboards & Reporting
- Integrations across endpoint, identity, cloud, network and security tools
- APIs & extensibility
DarkSense SOC+
DarkSense SOC+ delivers comprehensive 24/7 security monitoring, detection, investigation, and threat hunting, powered by the DarkSense platform and Arancia Security Operations Center. Unlike alert-only services, SOC+ provides centralized security telemetry and log management, giving organizations deep visibility across their environment while eliminating the complexity and cost of operating an internal SOC.
- 24/7 Security Monitoring
- SIEM & Log Management
- Security Data Retention
- Threat Detection & Correlation
- Alert Investigation & Triage
- Proactive Threat Hunting
- Threat Intelligence
- Incident Investigation Support
- Compliance Reporting
- Security Engineering Support
- SETAM (Security Engineer Technical Account Manager)
- Up to 12 months of searchable logs natively.
- Monthly Security & Service Reviews
DarkSense Alert+
DarkSense Alert+ provides cost-effective managed detection and response for organizations that already have security technologies generating high-quality alerts but do not require full SIEM log ingestion and retention.
Rather than ingesting every event, DarkSense centralizes, enriches, correlates, and investigates alerts from existing security technologies, providing expert oversight and automated response at a significantly lower infrastructure cost.
- 24/7 Alert Monitoring
- Alert Aggregation & Correlation
- Automated Enrichment
- Automated Response
- Analyst Investigation & Triage
- Expert-Guided Remediation
- Threat Intelligence
- Case Management
- Reporting
- Quarterly Security Reviews
DarkSense SOC+MDR
DarkSense SOC+MDR is our most comprehensive managed security offering, combining the visibility of a fully managed SOC with proactive threat hunting, advanced investigation, incident response, containment, and remediation. The Arancia security team operates as an extension of the customer's organization – not only identifying and escalating threats, but actively helping contain and resolve incidents.
- Everything included with DarkSense SOC+
- 24/7 Managed Detection & Response
- Proactive Threat Hunting
- Automated & Analyst-Driven Containment
- Incident Response
- Incident Remediation
- Digital Forensics
- Advanced Threat Investigation
- Detection Engineering
- Dedicated Security Team
- Ongoing Security Improvement
DarkSense Offerings at a Glance
Understand how each DarkSense offering supports different security operations needs, internal capabilities, and levels of managed support.
| Offering | What the customer buys | Who operates it | Best fit |
|---|---|---|---|
| DarkSense Platform | Cybersecurity operations platform / Next-Gen SIEM | Customer | Organizations with their own SOC |
| DarkSense Alert+ | Managed alert monitoring & response | Arancia | Customers wanting MDR without full log ingestion |
| DarkSense SOC+ | Platform + Fully managed SOC | Arancia | Organizations outsourcing SOC operations |
| DarkSense SOC+MDR | Fully SOC + active response/remediation | Arancia | Customers wanting end-to-end security operations |
Outcomes That Matter
Reduce Alert Noise
Correlate security signals and prioritize meaningful threats so analysts can focus on activity that requires action.
Detect & Investigate Faster
Combine telemetry, threat intelligence, AI, and automated investigation to accelerate threat detection and analysis.
Contain Threats Before They Escalate
Automate response and containment workflows to reduce the time between identifying malicious activity and taking action.
Reduce Cyber Risk Continuously
Connect detection and response with exposure and vulnerability management to move security operations from reactive monitoring toward continuous risk reduction.
Built for the Future of Security Operations
Unified Security Operations
Bring SIEM, SOAR, threat intelligence, investigation, threat hunting, exposure management, and response into one platform.
AI + Human Security Expertise
Combine AI-driven detection and automation with experienced security analysts and threat hunters.
Works Across Your Security Stack
Ingest and correlate telemetry across endpoint, identity, cloud, network, and other security technologies without requiring organizations to replace their existing investments.
Enterprise & MSSP Ready
Scale security operations across multiple customers, business units, and environments with built-in multi-tenant capabilities.
Move Beyond SIEM to Proactive Security Operations
See how DarkSense can unify your security operations, accelerate detection and response, and help your team continuously reduce cyber risk.